WireGuard is faster, lighter on battery, and small enough (~4,000 lines) that a security researcher can read all of it, while OpenVPN is heavier but runs over TCP port 443, so it still connects where WireGuard cannot. This wireguard vs openvpn explained guide breaks down both protocols on speed, security, setup and routing so you can pick the right one for your own network in 2026.
The short version for most people: default to WireGuard, keep OpenVPN as a fallback for networks that block UDP. Self-hosters reach that conclusion faster than almost everyone, because they hit the failure cases in week one.
Table of Contents
- WireGuard vs OpenVPN Explained: At a Glance
- What Is the Difference Between WireGuard and OpenVPN?
- Performance and Speed
- WireGuard vs OpenVPN performance in practice
- Security and Cryptography
- Configuration and Maintenance
- Compatibility and Platform Support
- Routing, DNS, and Network Behavior
- Which Should You Choose?
- Frequently Asked Questions
- Is WireGuard faster than OpenVPN?
- Is WireGuard more secure than OpenVPN?
- Should I use WireGuard or OpenVPN for a home lab?
- Can OpenVPN and WireGuard run on the same server?
- Why does WireGuard fail to connect on hotel or campus Wi-Fi?
- Conclusion
WireGuard vs OpenVPN Explained: At a Glance
| Criterion | WireGuard | OpenVPN |
|---|---|---|
| First released | 2015 development, merged into Linux kernel 5.6 in 2020 | 2001, still actively maintained |
| Creator | Jason A. Donenfeld | James Yonan and the OpenVPN team |
| Runs where | Inside the Linux kernel | User space, on top of OpenSSL |
| Code size | About 4,000 lines of kernel code | Roughly 100,000 lines plus the OpenSSL library it links against |
| Handshake | Noise protocol framework, one round trip | TLS handshake plus key negotiation |
| Encryption | ChaCha20-Poly1305, fixed suite | OpenSSL cipher suite, usually AES-256-GCM |
| Key exchange | Curve25519 | RSA or ECDSA certificates |
| Transport | UDP only | UDP or TCP, including TCP 443 |
| Typical throughput on a modern VPS | Several hundred Mbps up to the 1 Gbps range | Noticeably lower, especially without kernel offload |
| Connection setup time | Well under a second | Several seconds in many configurations |
| Peer authentication | Public key only, no certificates | Certificate authority hierarchy |
| Roaming between networks | Native, endpoint updates automatically | Needs configuration, works with reconnect logic |
| Fingerprintable by inspection | Yes, characteristic UDP packet shape | TCP 443 looks like ordinary web traffic |
| Best fit | Self-hosted, homelab, mobile, high throughput | Restrictive networks, legacy gear, wide interop |
One row in that table needs a word of explanation, because every competitor page gets it wrong. WireGuard’s ~4,000-line figure is consistent everywhere. OpenVPN’s is quoted as 70,000, 100,000+, or “hundreds of thousands,” and the spread is not a mistake: it depends on whether you count only the OpenVPN core, the core plus its management and client tooling, or the OpenSSL library OpenVPN calls into for every cryptographic operation.
What Is the Difference Between WireGuard and OpenVPN?
A VPN protocol is the rulebook your device and the VPN server both follow to build an encrypted tunnel. Both sides agree on keys, wrap each packet in an encrypted frame, and send it through; the protocol decides how that handshake happens and how fast the packets move afterwards.
WireGuard is the modern entry. Jason A. Donenfeld published it in 2015 and the design paper appeared at NDSS in 2017, and the implementation was merged into the Linux kernel in version 5.6 in 2020. It lives in kernel space, so packets are encrypted and decrypted without a copy into user space, and the whole implementation is small enough to review in an afternoon.
OpenVPN is the veteran. It came out in 2001, runs as a user-space process on top of OpenSSL, and carries two decades of options: certificates, plug-in modules, multiple authentication backends, site-to-site links, bridges, routed and bridged modes. It works over UDP or TCP, which matters more than most comparisons admit.
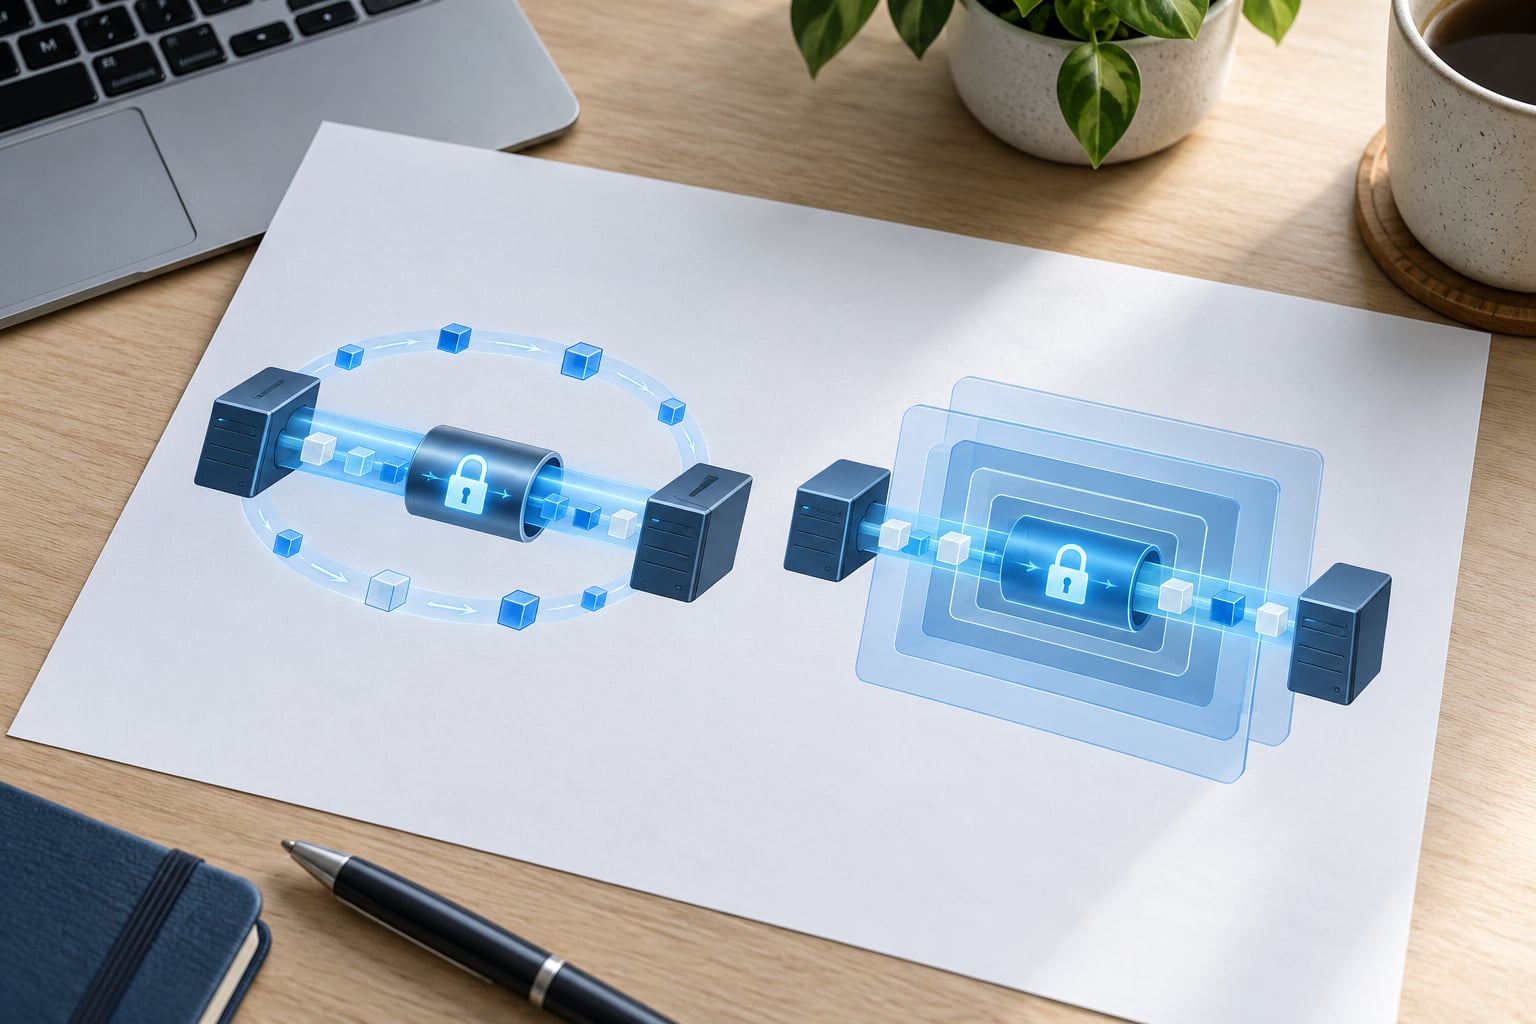
The architectural difference is worth holding on to. WireGuard is deliberately opinionated: it fixes one cipher suite and refuses to negotiate anything else, which removes an entire category of downgrade and misconfiguration bugs. OpenVPN is deliberately configurable, which buys you compatibility and costs you a bigger audit surface.
Performance and Speed
WireGuard is faster for four separable reasons, and if you only remember one, remember the first: it does its work in kernel space, so there is no context switch and no data copy for every packet.
That kernel placement also means packet processing stays cheap on mobile hardware. ChaCha20 is fast in software, so a phone does not need AES-NI instructions to keep up, and the CPU stays cool enough to matter on a phone battery.
The second reason is the handshake. WireGuard uses the Noise protocol framework and completes key exchange in a single round trip, so a connection is up almost immediately. OpenVPN performs a full TLS handshake and then negotiates its own data channel keys, which usually costs several seconds and is the difference between a tunnel that reconnects between two networks and one that shows a spinner.
The third reason is overhead. A WireGuard data packet carries a 16-byte authenticated header. An OpenVPN data packet is larger and its header is variable-length. On a slow mobile link the per-packet overhead is not the deciding factor, but it does add up on a busy transfer.
The fourth is roaming. WireGuard identifies peers by public key and updates the endpoint automatically, so moving from Wi-Fi to cellular does not tear down the tunnel. That shows up most in ping and in reconnects, not in a speed test.
WireGuard vs OpenVPN performance in practice
Here is where the honest caveats start. OpenVPN’s newer Data Channel Offload moves encryption into the kernel on Linux, which removes the user-space copy that used to be its biggest handicap. On a modern server with AES-NI hardware acceleration, AES-256-GCM is fast, and an OpenVPN server with DCO enabled on a well-peered link can come close to WireGuard on raw throughput.
Most published speed ranges on vendor pages are unsourced. You will see “50 percent faster,” “two to four times faster,” and “40 to 60 percent higher throughput” across three pages that all cite nobody. Treat those as marketing ranges, not measurements, and run your own test instead.
Benchmarking your own VPN is easy if you change one variable at a time. Measure throughput to the same target server with the tunnel off, then with the tunnel on, from the same location and time of day. Then change exactly one thing, such as MTU, and measure again.
While you are testing, watch for the classic self-inflicted problem: MTU. WireGuard defaults to an MTU of 1420 to account for its own header, and if your underlying path cannot carry a packet that size, you get fragmentation and throughput that looks inexplicably bad. Setting the MTU down until the symptom disappears usually fixes it in minutes.
The other half of the performance question is that the protocol is often not your bottleneck at all. Server distance, server CPU load, a saturated uplink, or poor ISP peering will swamp any difference between the two protocols. On a Raspberry Pi with a 100 Mbps uplink, both protocols will hit the uplink limit.
Security and Cryptography
WireGuard is considered secure because it is small enough to audit and modern enough by default: Curve25519 for key exchange, ChaCha20-Poly1305 for encryption, BLAKE2s for hashing, and HKDF for key derivation, all fixed at compile time rather than negotiated at runtime.
The handshake has also been the subject of formal verification work, which is unusual for a production VPN. The verification focuses on the Noise handshake logic and shows the protocol does what the design claims it does.
OpenVPN is secure by a different route: twenty-plus years of production use, wide review, and a cipher suite inherited from OpenSSL. The catch is scope. An OpenSSL dependency means you are shipping and patching an enormous cryptographic library as part of your VPN, and its history includes real incidents such as Heartbleed.
Forward secrecy deserves a precise answer for both. WireGuard rekeys on a timer and rotates ephemeral keys per session in a way that gives practical forward secrecy for the data channel. OpenVPN supports forward secrecy only when TLS is configured to use ephemeral key exchange, and that is not the default in a lot of deployments, so configuration matters.
Cipher agility cuts the other way. WireGuard’s fixed suite means a future weakness in ChaCha20 would require a protocol change rather than a config flag. OpenVPN can switch ciphers without that kind of break, which is a real advantage for a protocol that needs to live for another decade.
And WireGuard’s security story has a non-crypto limitation: it is UDP-only, and a blocked UDP port is a hard failure rather than a degraded one.
Configuration and Maintenance
Configuring WireGuard means generating keypairs and writing two numbers per peer. A minimal config is an interface section with a private key, a listen port, and one AllowedIPs line per peer; everything else is defaults, which is the whole appeal.
Configuring OpenVPN means a certificate authority, server and client certificates, a Diffie-Hellman parameter file, a TLS key, and a configuration file per client. That is genuinely more machinery, and it is why a lot of self-hosters quote setup simplicity rather than speed when they explain the switch. That day-to-day difference is the part of this wireguard vs openvpn explained comparison that actually costs you time.
At scale the gap changes shape. WireGuard’s config is small enough to template and hand to a phone by QR code or a short link. OpenVPN’s .ovpn files bundle certificates and keys, so distribution needs real attention: you either push them out securely or you end up emailing credentials to yourself.
Migrating is straightforward when you control the server, because you can run both protocols at once. Keep the OpenVPN server listening on TCP 443 for anyone on a restrictive network, add a WireGuard interface on a UDP port, and hand out WireGuard configs as the default. Most self-hosters arrive at that hybrid setup on their own once a peer fails to connect from a hotel.
Key rotation is where the philosophies collide. WireGuard peers are identified purely by public key, so rotating means generating a new keypair, updating the server’s AllowedIPs and endpoint, and pushing the new config. OpenVPN has a certificate infrastructure that handles expiry and revocation, which is a genuine advantage for organisations with a defined key lifecycle.
Compatibility and Platform Support
Both protocols run on Windows, macOS, Linux, Android and iOS. WireGuard has official apps for all five and most Linux distributions ship a client in their default repositories, so a fresh install on a Debian or Ubuntu machine is usually a single package.
OpenVPN’s client is older, more universal, and the only one that runs on a decade-old embedded device, a legacy NAS, or a corporate appliance whose vendor shipped OpenVPN and nothing else. That is not a hypothetical: it is why OpenVPN still holds enterprise deployments.
Router and appliance support is a bigger gap than it looks. Consumer routers from the major vendors still ship OpenVPN or their own VPN server, while WireGuard support depends on the firmware. OpenWrt and OPNsense both support WireGuard well; a stock router from a big brand may not.
One caveat about commercial providers: most do not ship vanilla WireGuard. NordVPN ships a WireGuard-derived protocol called NordLynx, and ExpressVPN ships Lightway. When you compare protocols through a provider’s menu, you are often comparing derivatives rather than the upstream implementations.
IKEv2/IPsec is the legitimate third option. It is comparable to WireGuard on speed, has built-in support for fast network handover through MOBIBE, and is the default on Apple platforms, but it is more painful to set up on Linux and awkward inside containers.
Routing, DNS, and Network Behavior
WireGuard routing is the part that surprises new users most, and it is really a design choice rather than a bug. The AllowedIPs field does double duty: it says which source addresses belong to that peer and which destination addresses should be routed to it. Set it too narrowly and traffic falls back to your normal gateway, which looks exactly like a DNS leak.
Full tunnel versus split tunnel is one line either way. AllowedIPs of 0.0.0.0/0 sends everything through the tunnel, which is what you want for privacy, and a single subnet such as 192.168.1.0/24 keeps everything else on the local link, which is what you want for a home lab.
DNS is where self-hosters lose the most time. The tunnel moves packets, not names, so a DNS server chosen before the tunnel came up will still be used after it. Setting a resolver inside the tunnel configuration fixes the leak and the slow first-page-load problem at the same time.
IPv6 works in both, and leaks in both if you are not careful. A tunnel configured for IPv4 only, on a network with native IPv6, sends IPv6 straight past the VPN. Blocking it in the firewall is part of setting either protocol up properly.
Port forwarding and CGNAT deserve a note because they come up constantly in self-hosting questions. If your home connection is behind carrier-grade NAT, the server cannot accept an incoming connection at all, and neither protocol changes that; you need a real public address or a relay. On a VPS with a public address, WireGuard’s simplicity makes port forwarding a two-line job, while OpenVPN needs a matching NAT rule in the client config.
Concurrent clients are a fair expectation-setting point. Both support many peers, and both are limited in practice by the server’s CPU and uplink rather than by the protocol, so an eight-core VPS will serve far more sessions than a Raspberry Pi regardless of which one you install.
The last behavioural difference is privacy. WireGuard retains a peer’s assigned internal IP in the server’s memory for the life of the connection, which sounds alarming and usually is not, since it is in-memory runtime state rather than a written log. Providers built around WireGuard have nonetheless responded to it, with some rotating keys on a weekly or 24-hour schedule so no single tunnel is long-lived.
Which Should You Choose?
Choose WireGuard when you control the server, when you want the tunnel to come back up fast after a network change, and when your clients are phones, laptops, and Raspberry Pis. Choose OpenVPN when you cannot rely on UDP, when you have to interoperate with old hardware, or when you need the authentication and certificate features that come with an enterprise deployment.
| Situation | Go with |
|---|---|
| Home lab with your own VPS | WireGuard, with OpenVPN on TCP 443 kept as fallback |
| Raspberry Pi as the VPN server | WireGuard, unless the Pi or the link is already saturated |
| Phone moving between Wi-Fi and cellular | WireGuard for roaming, battery life and reconnection speed |
| Corporate, campus or hotel network blocking UDP | OpenVPN over TCP 443 |
| Heavily inspected network | OpenVPN on TCP 443, or WireGuard wrapped in an obfuscation tool |
| Legacy appliance or old NAS | OpenVPN |
| Enterprise site-to-site with certificate lifecycle | OpenVPN or IKEv2/IPsec |
| Torrenting with port forwarding | Either; WireGuard for speed, OpenVPN if you rely on certificate-based access |
| Streaming services that geo-block by exit IP | Test both, since behaviour tracks the exit IP rather than the protocol |
If you are self-hosting and unsure, run both on the same box for a couple of weeks. WireGuard on a UDP port for daily use, OpenVPN listening on TCP 443 for the times someone cannot connect, and you will learn more from that fortnight than from any comparison page, including this one.
When you are behind deep packet inspection and UDP is also blocked, WireGuard itself has no answer, because adding a layer hides the shape rather than fixing the transport. Projects such as AmneziaWG modify the packet headers to defeat fingerprinting, and udp2raw wraps WireGuard datagrams in fake TCP or ICMP traffic. Both are real tools with real trade-offs, including their own performance cost.
Frequently Asked Questions
Is WireGuard faster than OpenVPN?
In most deployments, yes. WireGuard encrypts inside the Linux kernel, completes its handshake in a single round trip, and carries a smaller per-packet header, so throughput is higher and connections establish in well under a second instead of several. On a modern server with AES-NI and OpenVPN Data Channel Offload enabled, the raw throughput gap narrows considerably, and if the server or uplink is the bottleneck the protocol makes no measurable difference at all.
Is WireGuard more secure than OpenVPN?
WireGuard is generally easier to audit because it is about 4,000 lines of kernel code using a fixed modern suite: Curve25519, ChaCha20-Poly1305 and BLAKE2s. Its handshake has also been formally verified. OpenVPN is mature and widely reviewed, but its larger codebase and OpenSSL dependency mean a much bigger surface to keep patched.
Should I use WireGuard or OpenVPN for a home lab?
Choose WireGuard when your server runs a recent kernel or a platform with straightforward WireGuard support, and you want a two-line config. Choose OpenVPN when you need broad client compatibility, TCP fallback on a restrictive network, or certificate-based authentication for many users. Running both on one box is a perfectly normal answer.
Can OpenVPN and WireGuard run on the same server?
Yes. A Linux server can run both protocols on different listening ports, with separate interfaces, routes, firewall rules and key or certificate stores. This is the practical answer to migrating without cutting anyone off: default new clients to WireGuard and leave OpenVPN available on TCP 443 for anyone on a network that blocks UDP.
Why does WireGuard fail to connect on hotel or campus Wi-Fi?
WireGuard is UDP-only, so any network that blocks or throttles UDP will stop it connecting entirely rather than slow it down. OpenVPN over TCP 443 keeps working because that traffic looks like ordinary web traffic. If you must use WireGuard on such a network, an obfuscation wrapper such as AmneziaWG or udp2raw can help, at the cost of some throughput.
Conclusion
WireGuard is the better protocol for most people in 2026: faster, simpler, easier to audit, and built for the mobile, self-hosted setups most people actually run. OpenVPN keeps one advantage nobody can engineer away, which is TCP 443 fallback on networks that block UDP.
Before you commit, check four things in order. Confirm the clients you must support have implementations for your choice. Check whether your network permits UDP at all. Look at your existing infrastructure, since legacy gear often decides this on its own. Then set your performance expectations against your real link rather than a vendor’s chart.
If you want the primary sources behind this comparison, start with Donenfeld’s NDSS 2017 paper on WireGuard as a kernel network tunnel, the formal verification work on its handshake, RFC 7296 for IKEv2, and the OpenVPN project documentation.